


permission-flow is a macOS-first workspace for guiding users through system
permission onboarding from Rust apps.
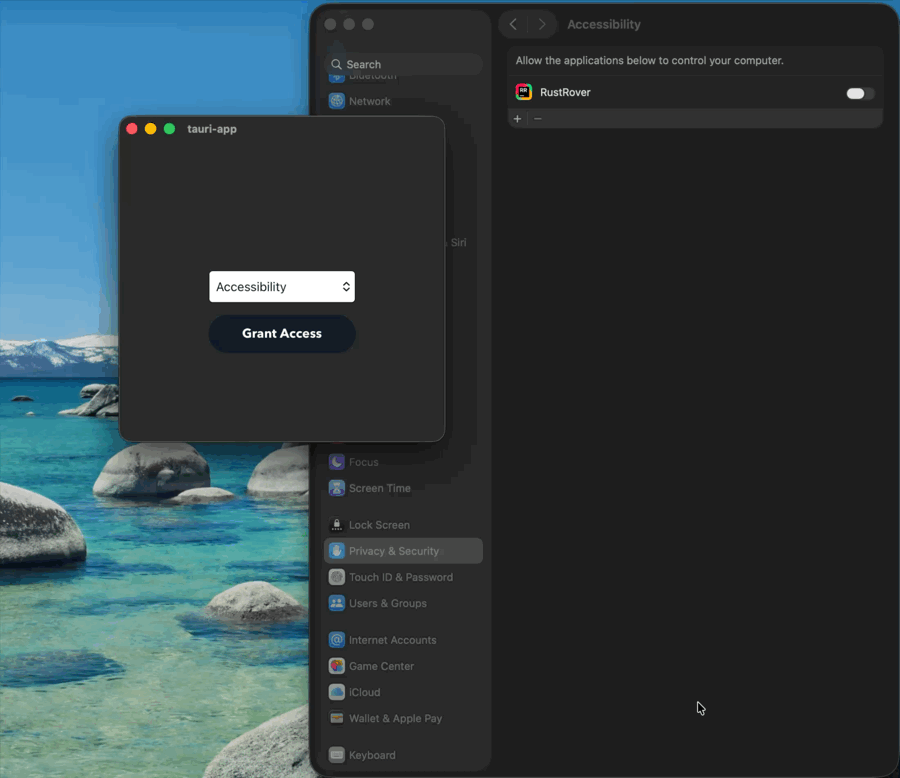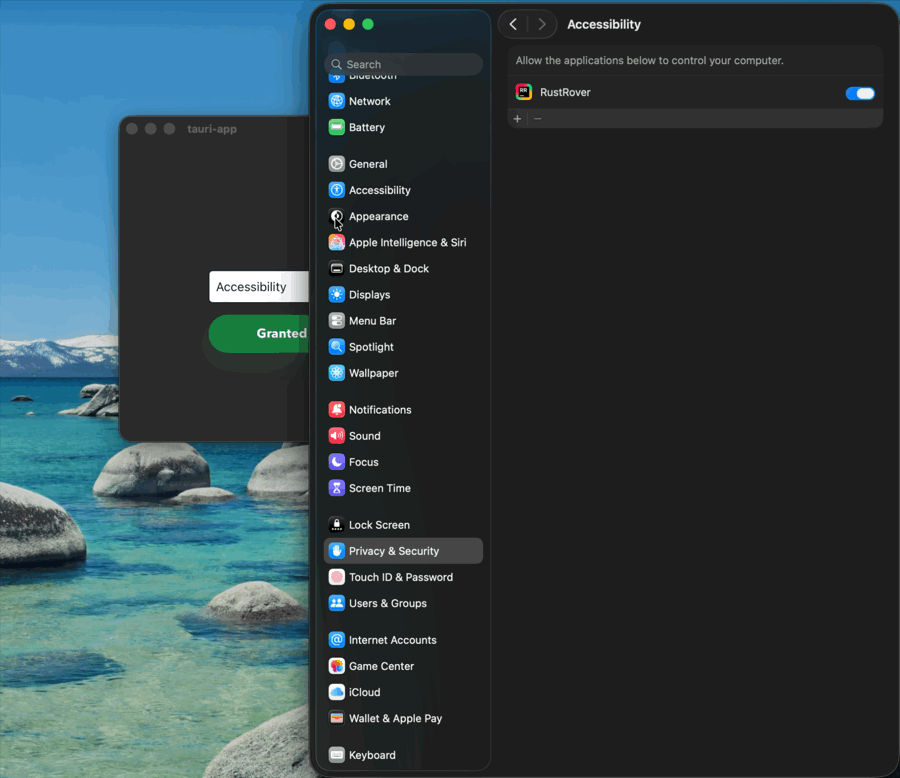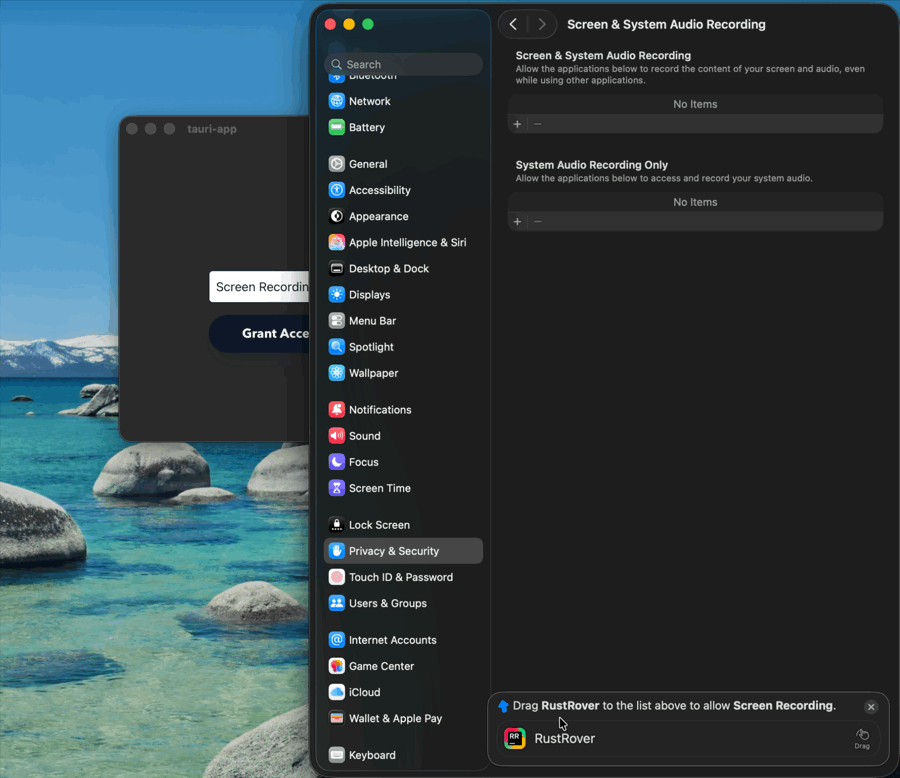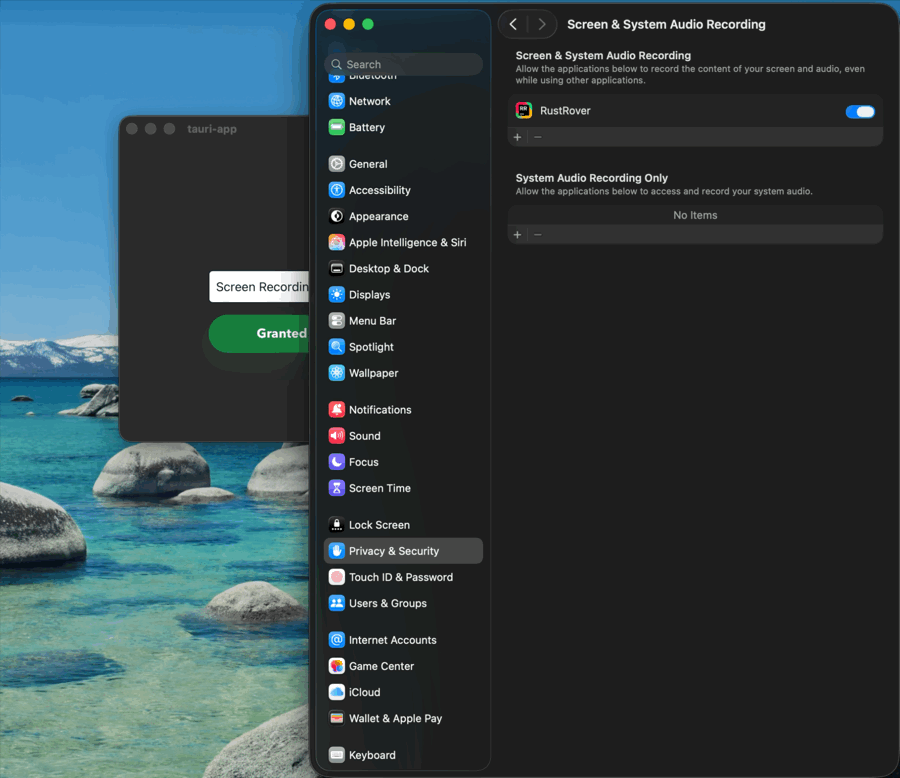
The workspace currently contains three packages:
permission-flow: the core Rust crate backed by the Swift/AppKit flowpermission-flow-iced: headlessicedhelpers built on top of the core cratetauri-plugin-permission-flow: a Tauri plugin plus guest-side JS bindings
Use permission-flow if you want direct Rust control over controller lifetime.
Use permission-flow-iced if you are building an iced app and want the
permission-flow and host-status wiring handled for you.
Use tauri-plugin-permission-flow if your UI lives in a Tauri frontend and you
want Rust plus JS bindings.
Add the core crate:
[dependencies]
permission-flow = "0.1.40"
Or use one of the higher-level packages:
[dependencies]
permission-flow-iced = "0.1.40"
tauri-plugin-permission-flow = "0.1.40"
The Tauri guest package is published separately on npm as:
{
  "dependencies": {
    "@veecore/tauri-plugin-permission-flow-api": "0.1.40"
  }
}The workspace supports guided flows for these permission areas:
- Accessibility
- Input Monitoring
- Screen Recording
- App Management
- Bluetooth
- Developer Tools
- Full Disk Access
- Media & Apple Music
The macOS flow is focused on:
- opening the right Settings area
- showing the target app bundle clearly
- guiding the user through the drag/drop step where needed
- giving you a host-app permission status signal you can reflect in your UI
The status helpers in this workspace describe what the current host app or host process can determine about its own permission state.
They do not authoritatively answer whether some arbitrary target .app
bundle already has that permission.
Because the final macOS executable links against Swift runtime libraries,
downstream binary crates currently need this in their build.rs:
fn main() {
    if std::env::var("CARGO_CFG_TARGET_OS").as_deref() == Ok("macos") {
        println!("cargo:rustc-link-arg=-Wl,-rpath,/usr/lib/swift");
    }
}- Core crate:
crates/flow/README.md - iced helpers:
crates/flow-iced/README.md - Tauri plugin:
crates/tauri-plugin-permission-flow/README.md
This workspace builds on top of the excellent
PermissionFlow Swift package
and uses swift-rs for the Rust to
Swift bridge.
The CI pipeline checks:
cargo fmt --all --checkcargo clippy --workspace --all-targets -- -D warningscargo test --workspace --libcargo check -p permission-flow-iced --examplescargo publish -p permission-flow --dry-run