Repository navigation
Blocking hallucinated and typosquatted packages with a BeforeTool hook #29954

Replies: 3 comments 1 reply

|
Answered my own question: Gemini CLI extensions can ship hooks in gemini extensions install https://github.com/somesh-ghaturle/pkg-guard --ref mainThe manual |

|
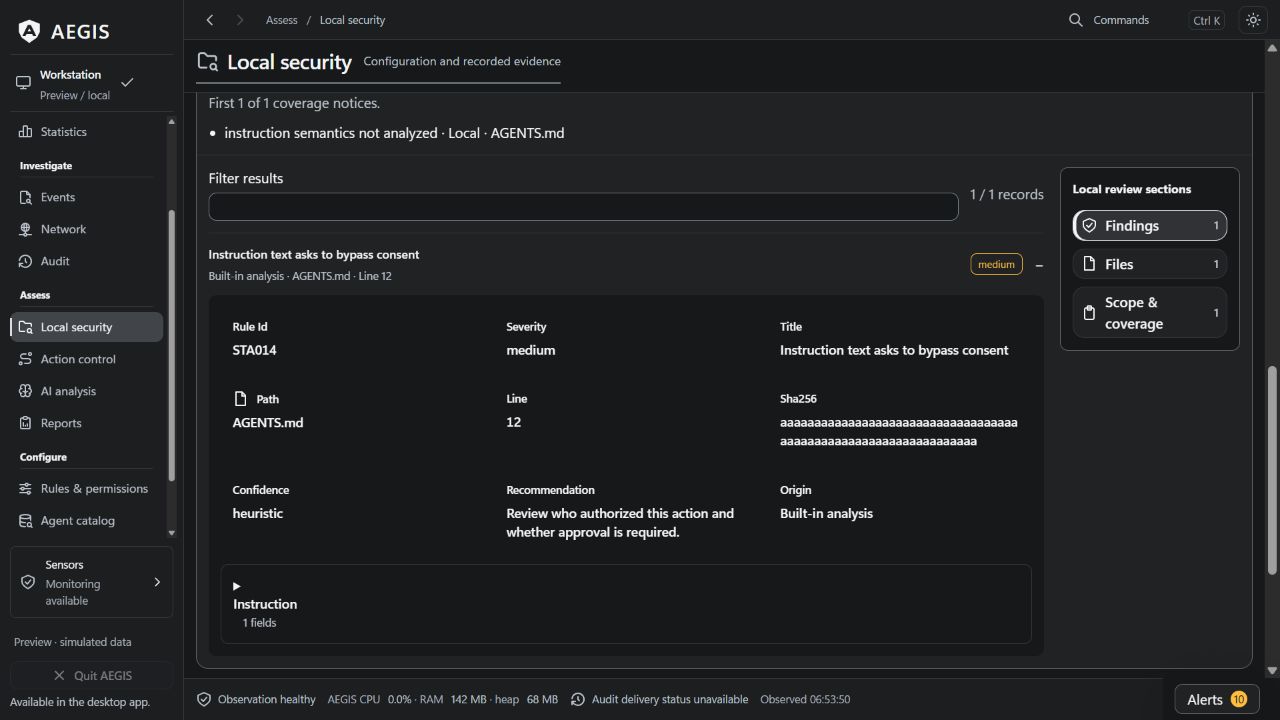
For false-positive feedback, I'd keep a reproducible decision table: a synthetic registry 404, a timeout, a valid newly published package, an explicitly allowlisted private name, and the same known-good package with cold/warm caches. Record the thresholds, allowlist, failure mode and cache state alongside the expected reason. That separates a policy choice or offline fallback from a heuristic regression without asking people to share private profile dumps. The registry responses can be fixtures; no real package installation is needed for that comparison. For the manual settings merge, recording the selected settings file before and after installation also helps distinguish configuration changes from package-decision changes. I maintain AEGIS at Escape Studio: its offline Gemini user/project review and saved inventory snapshot comparison support that selected-file check. It is an MIT Windows-first beta. Confirming which hook Gemini actually loaded remains a separate runtime check. Local security UI: 27 October 2026 source UI with simulated data; no live blocking test. |
|
Thanks, good checklist. Most of it is already covered with fixture responses (no network) in For false-positive reports, the most useful thing is the exact command plus the Update: v0.4.3 is released, so the extension now installs without gemini extensions install https://github.com/somesh-ghaturle/pkg-guard |

|
Thanks for the clarification and the fixture pointer. The stated network-failure mode and pass-only cache are important context for a report; I would include the configured mode and whether a result came from cache alongside the command and rule reason, with private names redacted before posting. I have not run pkg-guard, so this is not an independent test result. The selected-file inventory use case I mentioned stays separate from proving which extension/hook Gemini loaded and what happened to an attempted install. Thanks also for correcting the extension installation instructions. |


Uh oh!
There was an error while loading. Please reload this page.
Agents sometimes run
pip installornpm ion package names that don't exist, and attackers register those names ("slopsquatting"), along with one-letter typos of popular packages.I built pkg-guard, a
BeforeToolhook for Gemini CLI that checksrun_shell_command,write_fileandreplacecalls before they run. It blocks packages that are missing from the registry, one edit away from a popular package, under 30 days old, or barely used, and returns the reason so the agent fixes its own command:It covers npm, pnpm, yarn, bun, pip, uv, poetry, cargo, gem and go, and also checks dependencies the agent writes into manifests (
package.json,requirements.txt,pyproject.toml,Cargo.toml,go.mod, ...). Single Python file, stdlib only.Setup
Repo: https://github.com/somesh-ghaturle/pkg-guard
PyPI: https://pypi.org/project/slopsquat-guard/
A question for the maintainers: can a Gemini CLI extension ship a hook like this, so it installs with one
gemini extensions installcommand instead of a manual settings merge? Feedback on false positives is welcome too.All reactions